
.png)


(313 reviews)
AI Native Cyber Security & Ethical Hacking Career Track
৳৮,৮০০
ব্যাচ শুরু
শনিবার ৩১ অক্টোবর
৩১ অক্টোবর
লাইভ ক্লাস
রাত ৯:০০- ১০:৩০ (রবি,মঙ্গল)
সাপোর্ট ক্লাস


ক্লিক করে দেখে নিন কোর্সের ডেমো ক্লাস

Personal
একসাথে (Group)
৳৮,৮০০

ব্যাচ শুরু হতে সময় বাকি - 0d :0h :0m :0s
এই কোর্সে আপনি পাচ্ছেন:

৩০ সপ্তাহের স্টাডিপ্ল্যান
৫০টি লাইভ ক্লাস
প্রতি সপ্তাহে quiz ও assignment
প্রতি milestone শেষে exam
Capstone AI security agent ও demo day
Support class ও community support
Recording এ lifetime access
Interview handbook ও mock interview
Job placement support: CV, LinkedIn, GitHub review, referral
কোর্স সম্পর্কে:
Why this course is different
শুধু "AI-powered" নয়। সত্যিকারের AI Native।
- AI দিয়ে professional-দের মতো কাজ করুন। recon, SIEM alert triage, code review আর report draft করুন AI agent দিয়ে, আর কখন AI-কে বিশ্বাস করা যাবে না সেটাও শিখবেন।
- AI system hack করুন। chatbot, RAG app, AI agent আর MCP server test করবেন OWASP LLM Top 10 আর নতুন OWASP Top 10 for Agentic Applications দিয়ে।
- AI দিয়ে build করুন। Week 1 থেকেই live Python শিখবেন, আর নিজের একটা AI security agent বানিয়ে portfolio project হিসেবে ship করবেন।
What you will learn
চারটি milestone, একটি পরিষ্কার career path
- Foundations: Linux, live Python (basic থেকে security automation), networking ও traffic analysis, recon, scanning আর প্রথম lab exploit।
- Web, Code & API Security: OWASP Top 10, AI-assisted secure code review, REST ও GraphQL API testing।
- AI Security & Cloud: LLM app testing, agentic AI ও MCP security, Garak/PyRIT দিয়ে AI red teaming, AI governance, cloud security।
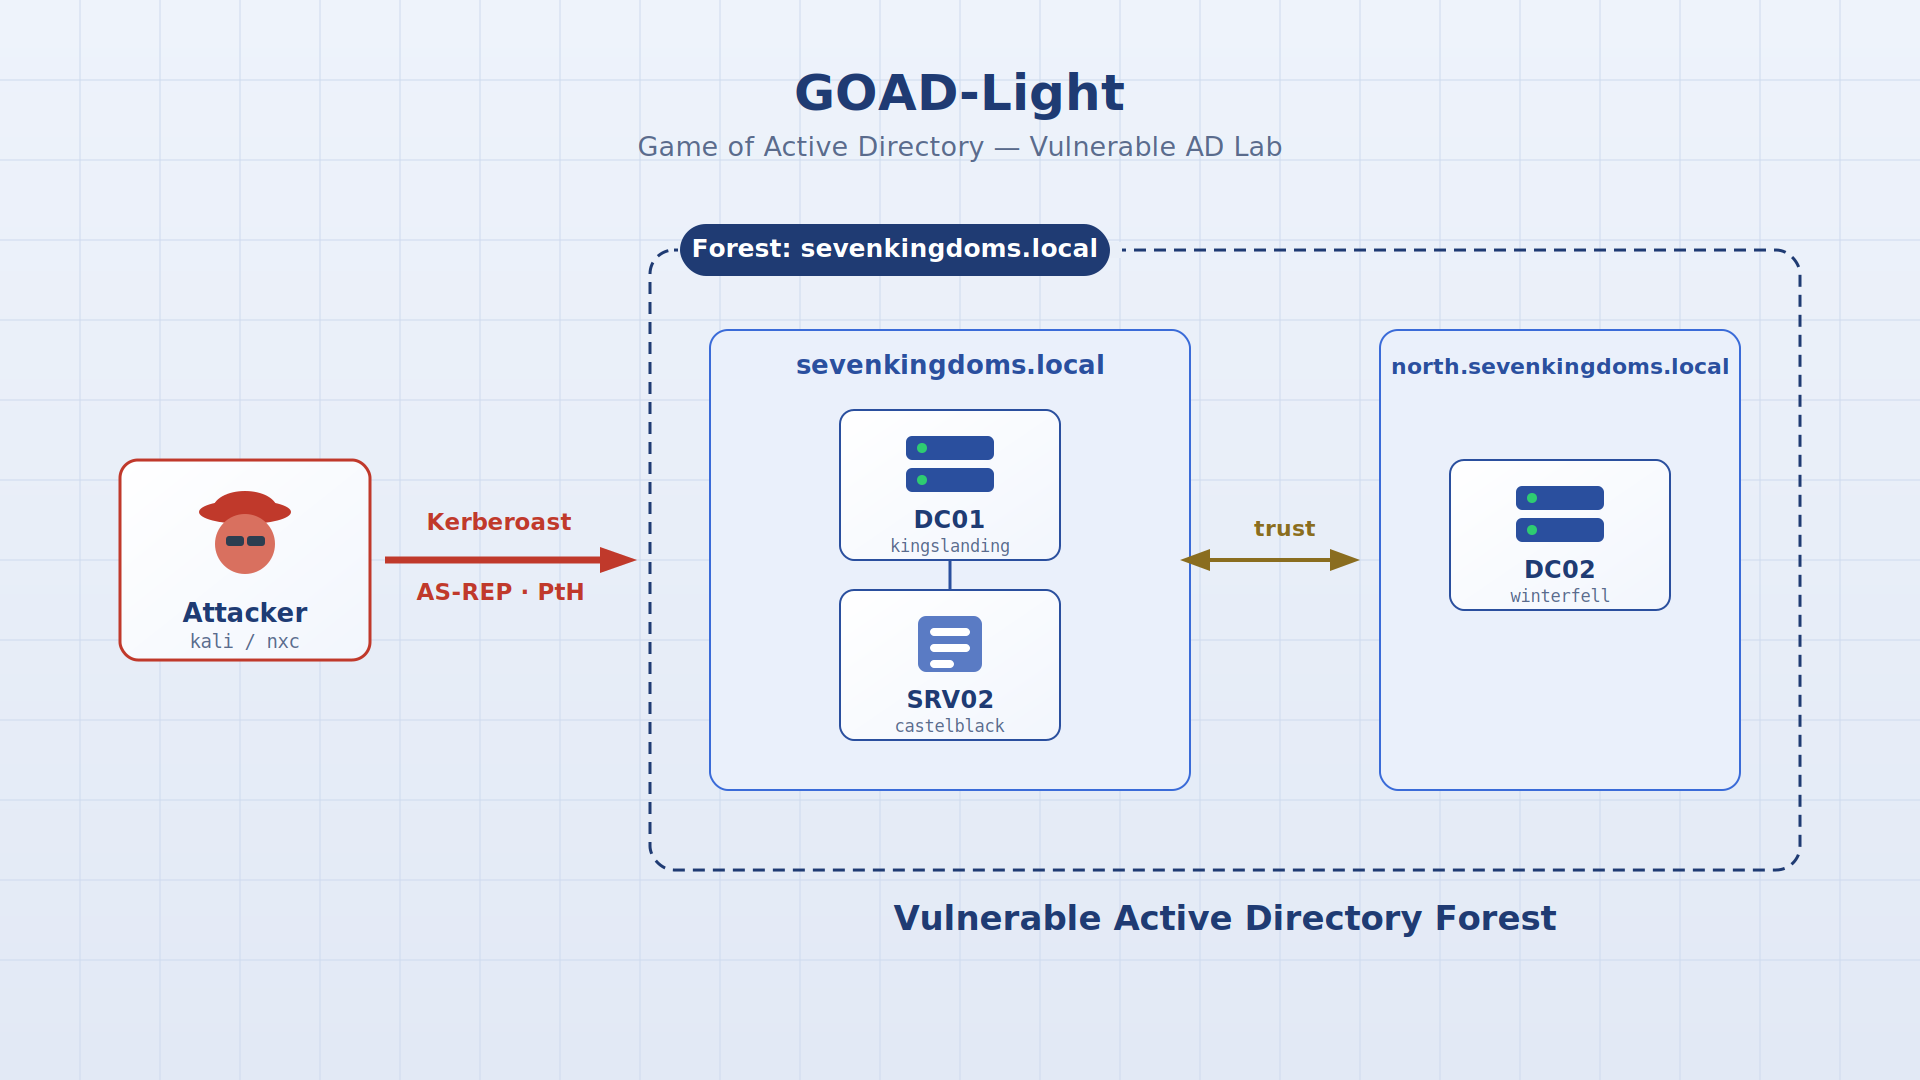
- Infrastructure, Defense & Career: privilege escalation, Active Directory, Wazuh দিয়ে AI-driven SOC, forensics, bug bounty আর reporting।
Hands-on practice
বেশিরভাগ lab-ই free, real lab এ practice করুন
PortSwigger Web Security Academy, OWASP Juice Shop, DVWA, OWASP crAPI, Damn Vulnerable MCP Server, Game of Active Directory, flaws.cloud, Wazuh আরও অনেক। কোনো lab platform এ টাকা খরচ না করেই পুরো course টা শেষ করতে পারবেন।
Who this is for
যাদের জন্য তৈরি
- একদম beginner, যারা cybersecurity তে career করতে চান
- যেকোনো background এর student ও graduate (CS হোক বা non-CS)
- IT ও network professional যারা security তে আসতে চান
- Developer যারা নিজেদের AI feature secure করতে চান
Career outcomes
- Junior Penetration Tester- SOC Analyst (L1)
- Bug Bounty Hunter
- Junior AI Security / AI Red Team Analyst
Certification path: eJPT, তারপর OSCP বা CRTE।

কারিকুলাম

কোর্সে আপনি পাচ্ছেন

প্রজেক্টসমুহ

কোর্সটি যাদের জন্য

জব পেয়েছে যারা

রিভিউ

FAQ

পেমেন্ট
কারিকুলাম
কোর্সে আপনি পাচ্ছেন
প্রজেক্টসমুহ
কোর্সটি যাদের জন্য
জব পেয়েছে যারা
রিভিউ
FAQ
পেমেন্ট
কোর্স করার আগে ডেমো ক্লাস করে দেখুন
প্রত্যেকটা সেকশনের কান্ট্রির বেস্ট ইন্সট্রাক্টরদের লাইভ ক্লাস কেমন হয়, দেখে নিন

Kali Linux মাস্টারক্লাস- Ethical Hackers দের জন্য

Sheikh Mohammad Adil
Penetration Tester | Ethical Hacker | Cyber Security Specialist at Bug Crowd

Bug Bounty Masterclass for Complete Beginners
Sheikh Mohammad Adil
Penetration Tester | Ethical Hacker | Cyber Security Specialist at Bug Crowd

Pentesting Masterclass for Cyber Security Aspirants

Safwan Muntasir
Security Analyst at Shorborno Holdings Limited
Mobile App Security Testing- MobSF, Mobexler & Report Analysis
Safwan Muntasir
Security Analyst at Shorborno Holdings Limited
লাইভ ডেমো ক্লাস
কোর্সে জয়েনের আগে লাইভ ডেমো ক্লাস করে নিন।
স্কিল্ড AI Driven Ethical Hacker হবার কমপ্লিট রোডম্যাপ ২০২৬: শূন্য থেকে জব রেডি
৬ অক্টোবর
রাত ৮:০০টা

১৫৬০ জন লাইভ ডেমো ক্লাসটি বুক করেছেন।
১৫৬০ জন লাইভ ডেমো ক্লাসটি বুক করেছেন।
কারিকুলাম
৩০ মডিউল
৫০ লাইভ ক্লাস
AI Security Foundations — Python, Law & Linux Mastery (Module 0-8)
ক্লাস নিবেনঃ

Safwan Muntasir
সপ্তাহ
০
AI-Powered Python for Cybersecurity Automation


58 recorded video
ব্যাচের কার্যক্রম - মেইন লাইভ ক্লাস শুরুর আগেই যারা ইনরোল করেছেন, তারা কি বসে থাকবেন? না! এই মডিউলে পাইথন এর বেশ কিছু ভিডিও দেওয়া আছে — AI টুলস দিয়ে কীভাবে সাইবার সিকিউরিটি অটোমেশন করবেন সেটাও শিখবেন। শুরু হয়ে যাক তবে শেখার জার্নি!
সপ্তাহ
২
Linux & Bash for Security Work

2 live class

1 Quiz

1 Assignment
Weekly goal: Navigate Kali, manage users and permissions, and automate a task with a Bash script.
Live Class 1: Kali Linux Fundamentals & Filesystem
Topic: Directory structure and navigation | File operations and permissions | Important system files | Package management
HANDS-ON LABS: TryHackMe: TryHackMe Linux Fundamentals Part 1, 2 and 3 rooms
Live Class 2: Users, Networking Commands & Bash
Topic: User and group management | Network commands: ip, ss, ping, traceroute | First Bash scripts | AI terminal assistants and checking their output
HANDS-ON LABS: Own machine / Replit: write a Bash script that pings a range and lists live hosts
সপ্তাহ
৪
Python for Security & AI Automation
2 live class
1 Quiz
1 Assignment
Weekly goal: Write a Python script that runs a scan, parses the output, and asks an LLM to summarise it.
Live Class 1: Python for Security
Topic: requests, socket, subprocess, json | Build a port checker and HTTP header grabber | Parse Nmap XML output into a clean report
HANDS-ON LABS: Own machine / Replit: build and run your own port checker and HTTP header grabber
Live Class 2: Calling LLMs from Python
Topic: LLM API basics, keys and cost control | Structured JSON output from a model | Mini project: AI recon summariser | Never send client data to public models
HANDS-ON LABS: Ollama with a local open model: build an AI recon summariser that reads Nmap output and writes a plain summary
Hosted LLM API key: optional, use a shared hosted key instead of a local model
সপ্তাহ
৬
Reconnaissance, OSINT & Social Engineering
2 live class
1 Quiz
1 Assignment
Weekly goal: Build a target profile (domains, people, emails, technology) using passive and active recon.
Live Class 1: Recon & OSINT
Topic: Active vs passive recon | OSINT framework and methodology | Search engine dorking and Whois | Automated recon tools
HANDS-ON LABS: TryHackMe: TryHackMe OSINT and Google Dorking rooms | Own machine / Replit: build a recon profile of your own domain with whois and subdomain tools
Live Class 2: Social Engineering in the AI Era
Topic: Phishing, spear phishing, vishing | AI-generated phishing and deepfake voice | Detection, awareness and defense
HANDS-ON LABS: TryHackMe : TryHackMe Phishing Analysis room
সপ্তাহ
৮
Exam Week 1
2 live class
1 Quiz
1 Assignment
মডিউল ১ থেকে মডিউল ৭ পর্যন্ত যা যা আলোচনা হয়েছে, সেটার উপর ভিত্তি করে থাকবে একটা বড়সড় এসাইনমেন্ট। ঝালিয়ে নিতে পারবেন নিজেকে।
সপ্তাহ
১
Cybersecurity Foundations, Law & How AI Works
2 live class
1 Quiz
1 Assignment
Weekly goal: Explain CIA, threat vs risk, legal scope, and how an LLM and an AI agent work.
Live Class 1: Foundations & Lab Setup
Topic: CIA triad; asset, threat, vulnerability, risk | Defense in depth and security principles | Lab build: Kali, Docker, Burp Suite | Create accounts: TryHackMe, PortSwigger, GitHub
HANDS-ON LABS: Kali Linux + VirtualBox/VMware: finish your Kali + Docker lab build and take a screenshot checklist
Live Class 2: Cyber Law, Ethics & AI Foundations
Topic: Bangladesh cyber law, scope and Rules of Engagement | Ethics of offensive AI tools | How LLMs work: tokens, context, system prompt | What an AI agent is: tools, memory, planning
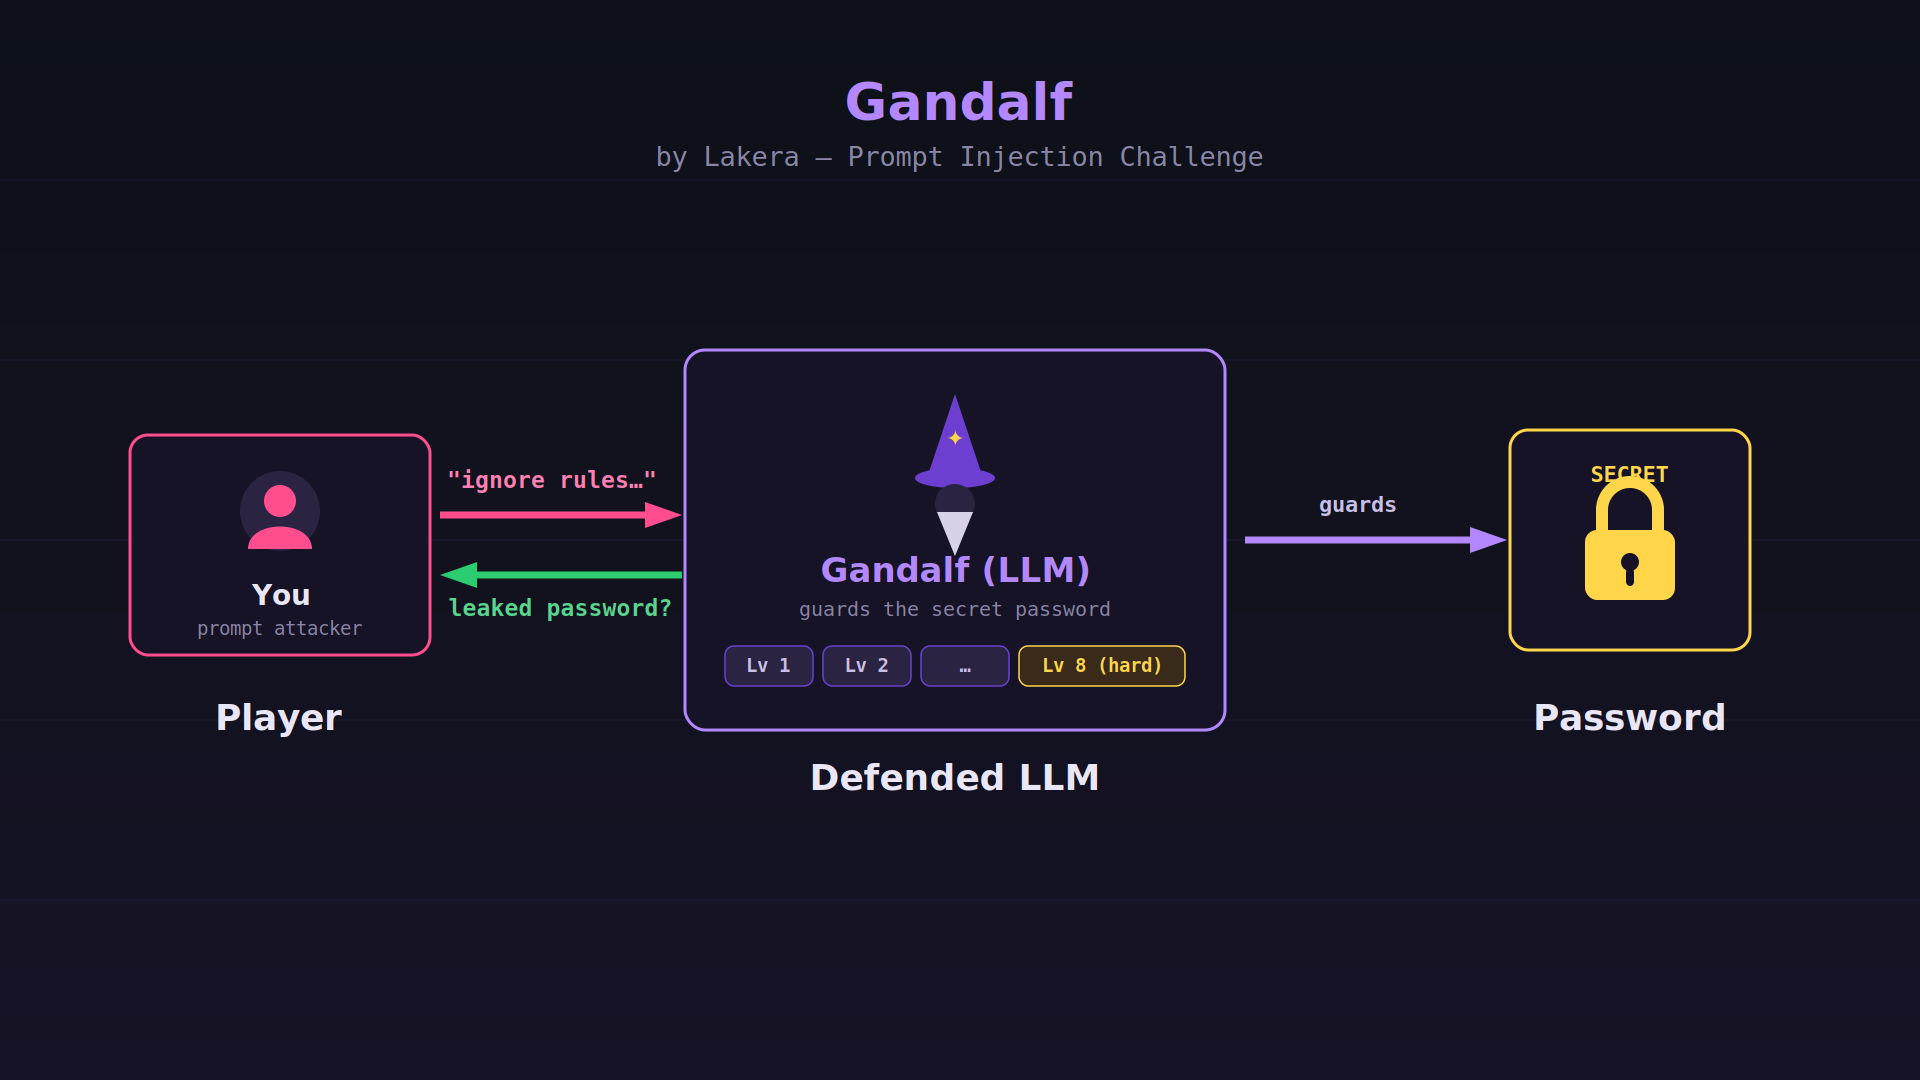
HANDS-ON LABS: Gandalf by Lakera: beat the first 4 Gandalf levels to see how prompts steer a model
TryHackMe Extra: TryHackMe Intro to Cyber Security path
সপ্তাহ
৩
Python Fundamentals (live)
2 live class
1 Quiz
1 Assignment
Weekly goal: Read and write basic Python with confidence: variables, loops, functions and files.
Live Class 1: Python Setup & Basics
Topic: Install Python and an editor | Variables, data types, strings | Lists and dictionaries | Input, output and simple programs
HANDS-ON LABS: Own machine / Replit: write 8 small programs (a calculator, a number guesser, a word counter)
Live Class 2: Logic & Reusable Code
Topic: Loops and conditions | Functions and modules | Files, JSON and error handling | Debugging your own script
HANDS-ON LABS: Own machine / Replit: write a script that reads a file of hosts and prints them cleanly
TryHackMe Extra: TryHackMe Python Basics room
সপ্তাহ
৫
Networking & Traffic Analysis
2 live class
1 Quiz
1 Assignment
Weekly goal: Read a packet capture and identify the protocol, the flow, and an attack pattern.
Live Class 1: Network Fundamentals
Topic: OSI and TCP/IP models | Ports and protocols | IP addressing, subnetting, CIDR | DNS resolution and network devices
Live Class 2: Packet Analysis with Wireshark
Topic: Capture and display filters | tcpdump and tshark | Spot SYN flood and amplification patterns in a pcap | Use AI to explain a capture summary
HANDS-ON LABS: TryHackMe: TryHackMe Wireshark The Basics and Nmap rooms | CyberDefenders: open a provided pcap and identify a port scan and a flood pattern
সপ্তাহ
৭
Scanning, Vulnerability Assessment & First Exploit
2 live class
1 Quiz
1 Assignment
Weekly goal: Scan a lab host, rate findings with CVSS, and exploit one known vulnerability.
Live Class 1: Network Scanning with Nmap
Topic: Scan types and service detection | OS detection and NSE scripts | AI-assisted triage of scan results
Live Class 2: From Assessment to Exploitation
Topic: Nessus and Nikto | CVE, CVSS and risk rating | Metasploit framework basics | Exploit a deliberately vulnerable lab VM
HANDS-ON LABS: Nessus Essentials: run a full Nessus scan on Metasploitable 2 and read the report Free Metasploitable 2: exploit one vulnerable service on Metasploitable 2 with Metasploit
VulnHub (Kioptrix series) Assignment: fully compromise Kioptrix Level 1
TryHackMe Extra: TryHackMe Vulnversity and Blue rooms
Web, Code & API Security (Module 9-17)
ক্লাস নিবেনঃ
.jpeg)
MD Sharior Akram
সপ্তাহ
৯
Cryptography & Web Foundations
2 live class
1 Quiz
1 Assignment
Weekly goal: Explain how TLS protects HTTP, and intercept and modify a request in Burp Suite.
Live Class 1: Cryptography Essentials
Topic: Symmetric (AES) and asymmetric (RSA) | Hashing, salting and password storage flaws | TLS handshake seen in Wireshark | Post-quantum cryptography overview
HANDS-ON LABS: Own machine / Replit: crack a provided list of weak password hashes with John the Ripper
Live Class 2: HTTP & Burp Suite
Topic: HTTP methods, headers, cookies, sessions | Burp Proxy, Repeater, Intruder | Build the web lab used in Weeks 9 to 14
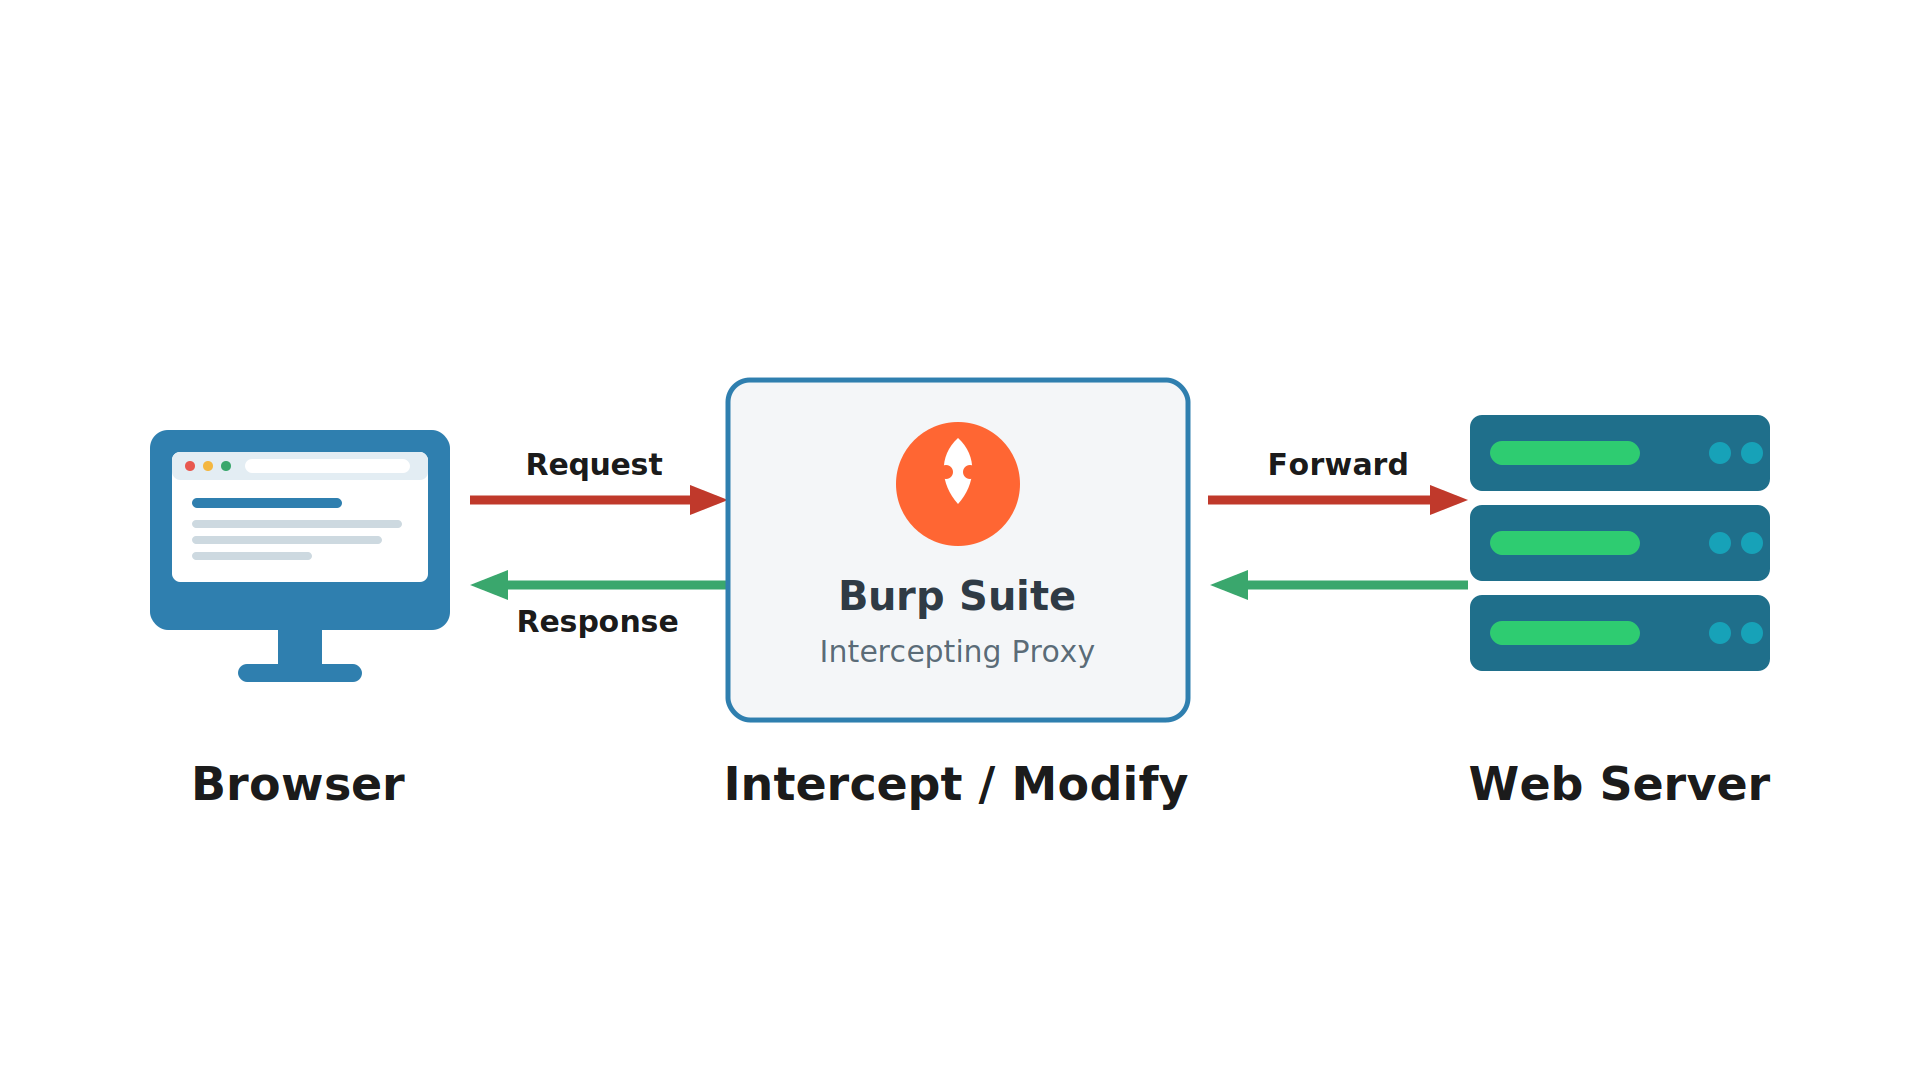
HANDS-ON LABS: Burp Suite Community: intercept and modify a request on Juice Shop with Burp Proxy | PortSwigger Web Security Academy: PortSwigger Burp Suite basics apprentice lab
সপ্তাহ
১১
File Inclusion & Upload Vulnerabilities
2 live class
1 Quiz
1 Assignment
Weekly goal: Identify and exploit file inclusion and file upload flaws in practice labs, and explain the
Live Class 1: File Inclusion
Topic: Path traversal concepts | Local and remote file inclusion | AI-assisted testing and filter awareness | Secure coding fixes
HANDS-ON LABS: PortSwigger Web Security Academy: PortSwigger Path traversal labs (all 6) | DVWA File Inclusion and File Upload at low and medium security
Live Class 2: File Upload Vulnerabilities
Topic: Unsafe upload patterns | Validation weaknesses | Impact and remediation
HANDS-ON LABS: PortSwigger Web Security Academy: PortSwigger File upload vulnerabilities labs | DVWA File Inclusion and File Upload at low and medium security
সপ্তাহ
১৩
XSS, CSRF & Client-Side Security
2 live class
1 Quiz
1 Assignment
Weekly goal: Find reflected, stored and DOM XSS and CSRF flaws in labs, and recommend CSP and SameSite fixes.
Live Class 1: JavaScript, DOM & XSS
Topic: DOM basics | Reflected, stored and DOM XSS | Session security impact
HANDS-ON LABS: PortSwigger Web Security Academy Class 1: PortSwigger Cross-site scripting labs (reflected, stored, DOM)
Live Class 2: CSRF & CSP
Topic: CSRF fundamentals | Token and SameSite protections | Content Security Policy basics
HANDS-ON LABS: PortSwigger Web Security Academy Class 2: PortSwigger CSRF labs
OWASP Juice Shop Extra: Juice Shop XSS challenges
সপ্তাহ
১৫
Misconfiguration, SSTI & Secure Code Review
2 live class
1 Quiz
1 Assignment
Weekly goal: Find misconfigurations in a running app, then find the same bug classes by reading its source code with AI help.
Live Class 1: Misconfiguration & SSTI
Topic: CORS misconfiguration | Default credentials and exposed panels | Security headers and subdomain takeover | Server-side template injection
HANDS-ON LABS: PortSwigger Web Security Academy: PortSwigger CORS and SSTI labs
Live Class 2: AI-Assisted Secure Code Review
Topic: Reading Flask, Django and Node.js code for common bugs | Using AI to review code and verifying its findings | Semgrep basics
HANDS-ON LABS: Semgrep Community Edition: scan the Ostad vulnerable Flask/Django repo and triage the findings | Vulnerable Flask/Django app (Ostad repo): locate three real bugs in the source, then confirm them in the running app
সপ্তাহ
১৭
Exam week 2
1 Assignment
মডিউল ৯ থেকে মডিউল ১৬ পর্যন্ত যা যা আলোচনা হয়েছে, সেটার উপর ভিত্তি করে থাকবে একটা বড়সড় এসাইনমেন্ট ও লাইভ টেস্ট। ঝালিয়ে নিতে পারবেন নিজেকে।
সপ্তাহ
১০
Web Recon & OWASP Top 10
2 live class
1 Quiz
1 Assignment
Weekly goal: Map a web app's attack surface and classify findings against the OWASP Top 10.
Live Class 1: Web Attack Surface Discovery
Topic: Subdomain enumeration | Directory and content discovery | Technology fingerprinting | Automating recon with a Python script
HANDS-ON LABS: OWASP Juice Shop: find and log 5 bugs across different OWASP Top 10 categories in Juice Shop
Live Class 2: OWASP Top 10 Walkthrough
Topic: Each category with one live lab example | Detection approach per category
HANDS-ON LABS: find and log 5 bugs across different OWASP Top 10 categories in Juice Shop | PortSwigger Web Security Academy: PortSwigger Information disclosure apprentice labs
সপ্তাহ
১২
SQL Injection
2 live class
1 Quiz
1 Assignment
Weekly goal: Find and confirm SQL injection in practice labs and recommend parameterised queries.
Live Class 1: SQL & SQLi Fundamentals
Topic: SQL basics | SQLi types: in-band, error-based, blind | Finding injection points
HANDS-ON LABS: PortSwigger Web Security Academy: PortSwigger SQL injection labs (UNION and blind sets) | DVWA SQL Injection and Blind SQL Injection modules
Live Class 2: Advanced SQLi & Tooling
Topic: UNION and blind techniques in labs | sqlmap with manual validation | WAF awareness and defense
HANDS-ON LABS: PortSwigger Web Security Academy: PortSwigger SQL injection labs (UNION and blind sets)
সপ্তাহ
১৪
SSRF, XXE, Business Logic & Authentication
2 live class
1 Quiz
1 Assignment
Weekly goal: Find SSRF, XXE and a business logic flaw in a lab app.
Live Class 1: SSRF & XXE
Topic: SSRF concepts and internal service access | Cloud metadata risk | XXE detection and remediation
HANDS-ON LABS: PortSwigger Web Security Academy: PortSwigger SSRF and XXE labs
Live Class 2: Business Logic & Authentication
Topic: Logic flaws: price tampering, workflow skip, race conditions | Password attacks and wordlists in labs | Missing rate limits and app-layer DoS (concept only)
HANDS-ON LABS:PortSwigger Web Security Academy Class 2: PortSwigger Business logic vulnerabilities and Race conditions labs
সপ্তাহ
১৬
API Security
2 live class
1 Quiz
1 Assignment
Weekly goal: Test a REST and a GraphQL API and report authorisation and authentication findings.
Live Class 1: API Fundamentals
Topic: REST and GraphQL | API keys, JWT, OAuth 2.0 | Rate limiting and versioning | API attack surface mapping
HANDS-ON LABS: OWASP crAPI: complete the crAPI BOLA, broken authentication and mass assignment challenges
Live Class 2: API Vulnerability Testing
Topic: BOLA and IDOR | Broken authentication and token flaws | Excessive data exposure | Postman and Burp for API testing
HANDS-ON LABS: OWASP crAPI: complete the crAPI BOLA, broken authentication and mass assignment challenges | PortSwigger Web Security Academy: PortSwigger API testing and JWT labs
AI Security & Cloud (Module 18-22)
ক্লাস নিবেনঃ
MD Sharior Akram
সপ্তাহ
১৮
LLM Application Security Testing
2 live class
1 Quiz
1 Assignment
Weekly goal: Test a RAG chatbot for prompt injection and write the finding in OWASP LLM Top 10 terms.
Live Class 1: How LLM Apps Are Built & Broken
Topic: System prompt, context window, RAG, tool calls | OWASP Top 10 for LLM Applications (2025) in depth | Where classic web bugs reappear in AI features
HANDS-ON LABS: Ollama with a local open model: build a small RAG chatbot, then try to make it reveal its system prompt
Live Class 2: Prompt Injection Lab
Topic: Direct and indirect prompt injection | System prompt leakage | Insecure output handling | Defenses and their limits
HANDS-ON LABS: PortSwigger Web Security Academy: PortSwigger Web LLM attacks labs (all in the path)
Gandalf by Lakera Extra: clear the advanced Gandalf levels
সপ্তাহ
২০
AI Red Teaming & AI Governance
2 live class
1 Quiz
1 Assignment
Weekly goal: Run an automated scan on a model endpoint and map results to MITRE ATLAS and a governance framework.
Live Class 1: AI Red Teaming Tools
Topic: Garak and PyRIT | Jailbreak and data leakage probes | MITRE ATLAS tactics | Threat modelling an AI feature
HANDS-ON LABS: Garak (LLM vulnerability scanner): run the Garak probe set against a local Ollama model and read the report | PyRIT (AI red teaming toolkit): run a jailbreak probe batch with PyRIT
Live Class 2: Security & AI Governance
Topic: ISO 27001, NIST CSF, PCI DSS overview | Bangladesh Bank ICT Security Guideline | NIST AI RMF and ISO/IEC 42001 | Write an AI risk register for a fintech chatbot
HANDS-ON LABS: Own machine / Replit: write an AI risk register for a sample fintech chatbot
সপ্তাহ
২২
Exam week 3
1 Assignment
মডিউল ১৮ থেকে মডিউল ২১ পর্যন্ত যা যা আলোচনা হয়েছে, সেটার উপর ভিত্তি করে থাকবে একটা বড়সড় এসাইনমেন্ট ও লাইভ টেস্ট। ঝালিয়ে নিতে পারবেন নিজেকে।
সপ্তাহ
১৯
Agentic AI & MCP Security
2 live class
1 Quiz
1 Assignment
Weekly goal: Assess a tool-using agent for misuse and data leakage, and propose least-privilege fixes.
Live Class 1: OWASP Agentic Top 10 (2026)
Topic: Agent goal hijack and tool misuse | Identity and privilege abuse | Memory and context poisoning | Agentic supply chain and cascading failures
Live Class 2: MCP & Agent Security Lab
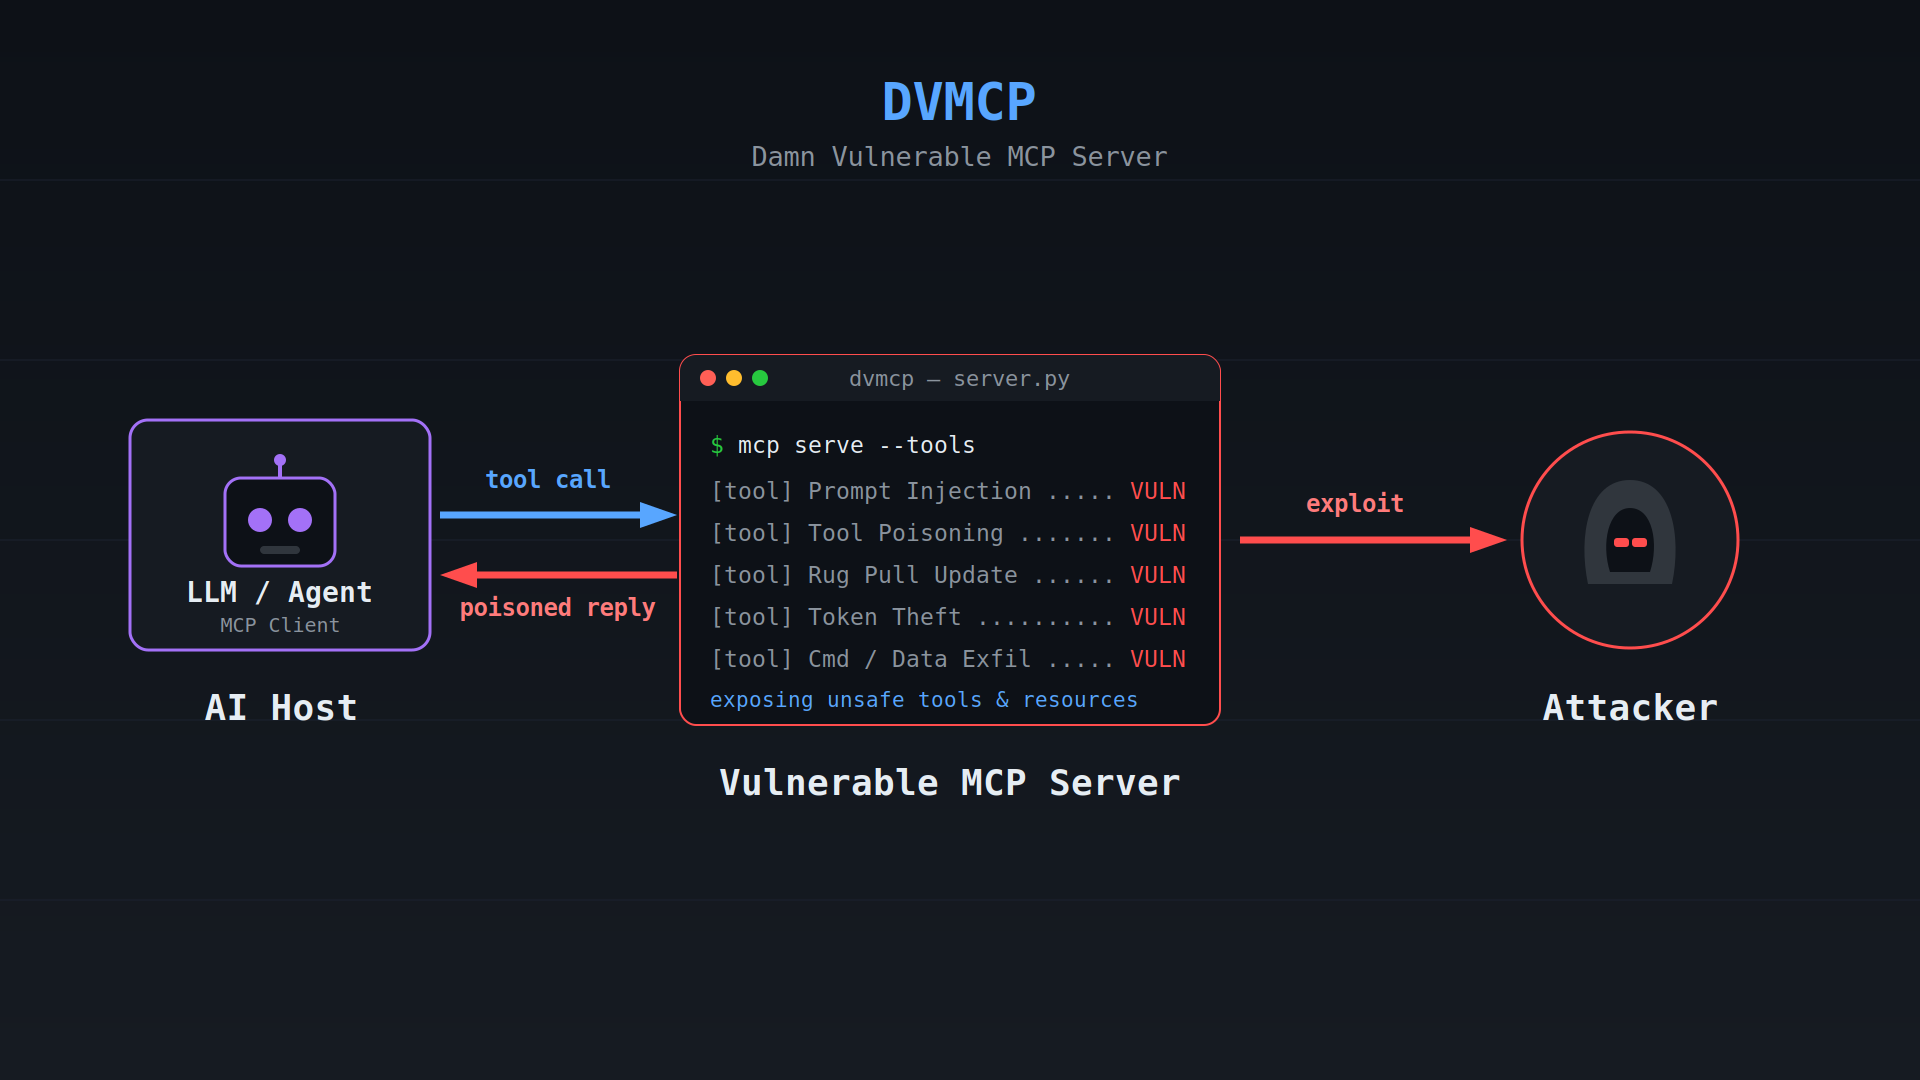
Topic: How MCP servers expose tools | Testing tool permissions and over-scoped tokens | Poisoned content steering an agent | Mitigation: least privilege, sandboxing, human approval
HANDS-ON LABS: Damn Vulnerable MCP Server (DVMCP): solve the DVMCP challenges on tool poisoning and excessive permissions | Ollama with a local open model: build a tool-using agent, then show an over-scoped tool leaking data
সপ্তাহ
২১
Cloud Security
2 live class
1 Quiz
1 Assignment
Weekly goal: Find an IAM or storage misconfiguration in a cloud lab and secure an AI model endpoint.
Live Class 1: Cloud Fundamentals for Testers
Topic: IaaS, PaaS, SaaS and shared responsibility | IAM, storage, compute, VPC, security groups | Common cloud misconfigurations
HANDS-ON LABS: flaws.cloud and flaws2.cloud: complete all levels of flaws.cloud and flaws2.cloud
Live Class 2: Cloud Assessment & AI Workloads
Topic: Enumeration with cloud CLI tools | Over-privileged roles, public buckets, leaked keys | Securing model endpoints, secrets and API keys
HANDS-ON LABS: flaws.cloud and flaws2.cloud: complete all levels of flaws.cloud and flaws2.cloud
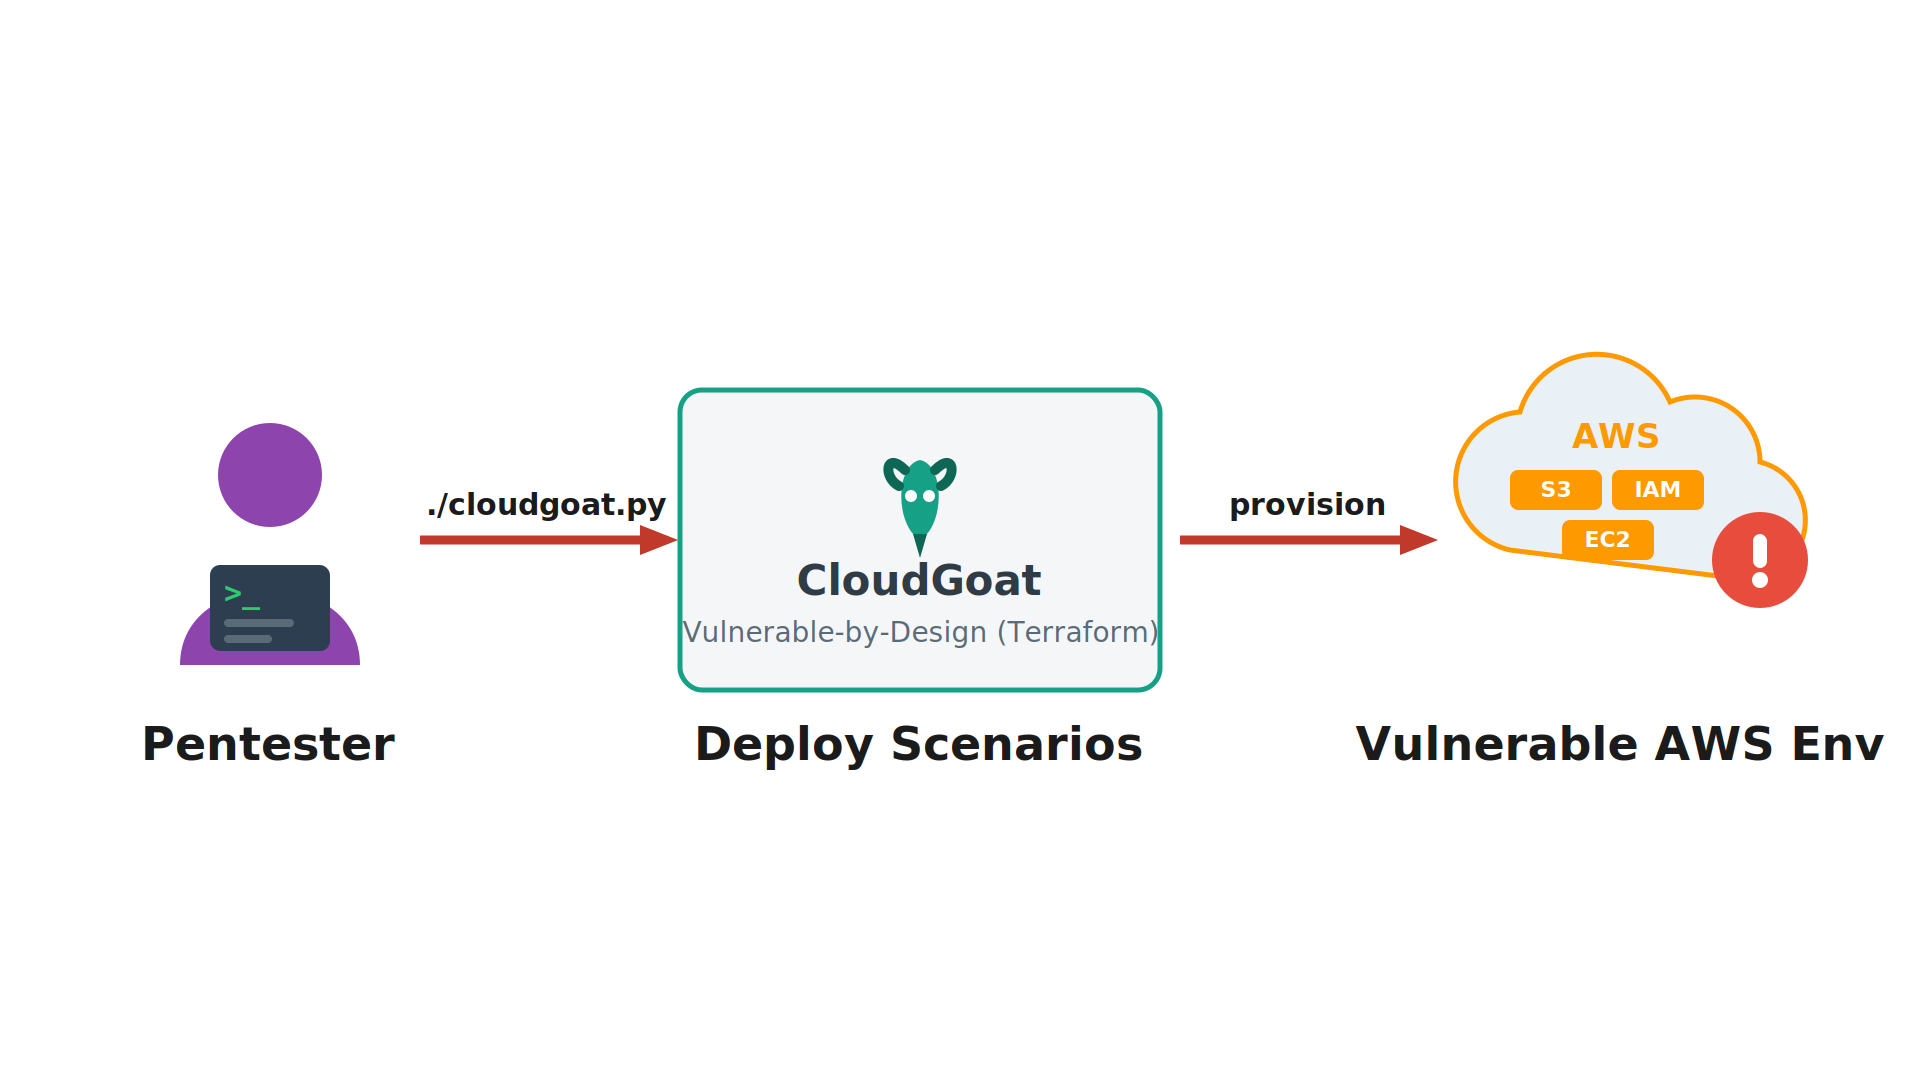
CloudGoat Extra: run one CloudGoat scenario in your own AWS account
কোর্সটি আপনারই জন্য

ইন্সট্রাক্টর

SHEIKH MOHAMMAD ADIL
Penetration Tester | CRTA | Bug Bounty Hunter | Cybersecurity & Offensive Security Specialist


Safwan Muntasir
Security Analyst - Threat Detection and Response (Cyber Fusion Center) at Shorborno Holdings Limited | ex- Smart Technologies | Augmented Resource at Grameenphone
MD Sharior Akram
Engineer, Cybersecurity at Smart Technologies (BD) Limited | Senior Advisor, ICSS at IU Cyber Security Society | Assistant Researcher, Cybersecurity at ICE Innovation Lab, Islamic University | Former Assistant Officer, Cybersecurity at Akij Blue Pill Limited
.png)
.png)

Dipto Dutta
CyberTech Shield LLC

Tarek Monoar
Teaching Assistant (TA) at Ostad | Hands-on Trainee at TryHackMe | Junior Penetration Tester | Cyber Security Analyst | Ethical Hacking Practitioner | Web Security Researcher

.png)

যেসব ট্যুলস ও টেকনোলোজি শিখবেন
.png)
Kali Linux
.png)
VMware

Docker
Ollama
.jpeg)
tcpdump/tshark
.jpeg)
John the Ripper

VirtualBox
.jpeg)
Semgrep
.png)
ANY.RUN
Garak
Autopsy
.png)
Wazuh
.png)
BloodHound
Nessus
Metasploit
MobSF
Mobexler

Wireshark
Burp Suite

Postman

GitHub
Putty
Nmap
.jpg)
Nikto
SQLMap
TryHackMe
VulnHub

Linux
NIST
PCI DSS
.png)
CVSS
.png)
PyRIT
.png)
Volatility
.png)
LinPEAS / WinPEAS
কী কী থাকতে হবে

ল্যাপটপ/ডেস্কটপ (৮ জিবি র্যাম)

ভালো ইন্টারনেট কানেকশন

লেগে থাকার মানসিকতা
কোর্সে আপনি পাচ্ছেন

৭ মাসের স্টাডিপ্ল্যান

৫০ টি লাইভ ক্লাস

২৫+ টি ইন্ডাস্ট্রি স্ট্যান্ডার্ড প্রজেক্ট

প্রোগ্রেস ট্র্যাকিং

সপ্তাহে ৩ দিন সাপোর্ট ক্লাস

কমিউনিটি সাপোর্ট

লাইফটাইম এক্সেস

ইন্টারভিউ হ্যান্ডবুক

সার্টিফিকেট
কোর্স শেষে পাচ্ছেন এক্সক্লুসিভ জব প্লেসমেন্ট সাপোর্ট!


.png)
কোর্সটি আপনারই জন্য
সাকসেসফুল হয়েছেন যারা
ফিডব্যাক
আমাদের লার্নারদের কাছে শুনুন
Ostad provided an excellent environment to learn, practice, and apply real-world cybersecurity concepts. The experience played a significant role in my professional growth, and I'm grateful to continue contributing to the community as a Teaching Assistant.
MT
Md. Tarek Monoar

Ostad's live and interactive learning methodology completely changed my upskilling journey. Mastering any complex skill is now very practical due to their specific and industry-focused curriculum. Real-time guidance and support from mentors helped me move forward with confidence at every step. In short, Ostad is truly a next-level platform to boost careers and learn in-demand skills
SR
Sheikh Rasel Mehedi
ওস্তাদ আমার কাছে সেরা একটি প্ল্যাটফর্ম মনে হয়েছে। আমি ইতোমধ্যে আপনাদের অন্য একটি ব্যাচেও এনরোল্ড আছি, এবং সামগ্রিকভাবে আপনাদের ম্যানেজমেন্টকে খুব গোছানো ও চমৎকার লেগেছে। আপনাদের ম্যানেজমেন্ট ও সাপোর্ট সিস্টেম দুর্দান্ত।
AI
Ariful Islam
কোর্সটি খুবই ভালো ছিলো। অনেক নতুন কিছু শিখতে পেরেছি যা আমার জন্য খুবই উপকারি হয়েছে।
TA
Tahsin Arafat
কোর্সটি অনেক ভালো ছিল। আমি আসলে নিজের ক্যারিয়ার গঠনের জন্য এই কোর্সটা করেছি এবং এখান থেকে অনেক কিছু শিখেছি।
SA
Sharmin Akter
এই কোর্সটি আমার জন্য অনেক সহায়ক ছিল। বিশেষভাবে, তাদের শেখানোর পদ্ধতি এবং ম্যানেজমেন্ট আমাকে খুবই প্রভাবিত করেছে।
SN
Suhana Nargis
ওস্তাদের ক্লাসের মাধ্যমে আমি অনেক নতুন ধারণা শিখেছি যা আমার কাজে অনেক সাহায্য করেছে। কোর্সটি ছিল অনেক কার্যকরী।
TS
Tuhin Saha
কোর্সটি সত্যিই খুব ভালো ছিল। এর শিক্ষণ পদ্ধতি এবং উপস্থাপনা খুব পরিষ্কার ছিল, যা আমার শেখার অভিজ্ঞতাকে সহজ করে তুলেছে।
MS
Mariam Sultana
আমি কোর্সটি করার পর, নিজের স্কিল উন্নতির ব্যাপারে অনেক কিছু বুঝতে পেরেছি। কোর্সটি সত্যিই কার্যকর ছিল।
KH
Kaisar Hossain
বিগিনার থেকে ইন্টারমিডিয়েট লেভেল পর্যন্ত শেখার জন্য এই কোর্সটি আমার কাছে সত্যিই দারুণ লেগেছে। আমি চেষ্টা করছি ভালোভাবে কোর্সটি সম্পন্ন করতে, এবং নিয়মিত কুইজ, অ্যাসাইনমেন্ট ও ক্লাসের মাধ্যমে প্র্যাকটিস করে যাচ্ছি। আমাদের ইনস্ট্রাক্টর অত্যন্ত সাপোর্টিভ ছিলেন — জটিল বিষয়গুলোও সহজভাবে বুঝিয়ে দিয়েছেন। সবকিছু মিলিয়ে, বিগিনার ও ইন্টারমিডিয়েট লেভেলের জন্য এই কোর্সটি বেশ সহায়ক বলে আমার মনে হয়েছে
NU
Nazim Uddin Tarif
Clear explanation, very knowledgeable Course Instructors.
RI
Redwan Islam (ব্যাচ ৯)
Supportive, talkative, narrative.
AC
Anik Chowdhury (ব্যাচ ৮)
The Course Instructors have vast knowledge about CS. I am optimistic that we will get better information from them.
BH
Bellal Hossain (ব্যাচ ১০)
Course Instructors onk valo bujate pare.
SA
Shah Amin (ব্যাচ ১০)
Course Instructors খুব ভালো করে পড়ান এবং তাঁদের বোঝানোর সক্ষমতা অনেক।
RA
Raju Ahmed (ব্যাচ ৯)
The Course Instructors are very helpful and knowledgeable.
RB
Rifat Bin Tayub (ব্যাচ ৯)
The Course Instructors are very friendly and respectful when listening. I am very happy with them. I understand everything that they explain.
AN
Al Nasif Farhan (ব্যাচ ৮)
The Course Instructors make a sincere effort to align examples with the topic, which is a positive aspect of the sessions.
SY
Samin Yaser Ayon (ব্যাচ ৮)
The Course Instructors are outstanding. They clearly know our problems and solve them very well.
MR
Mohammad Raseduzzaman Khan (ব্যাচ ৮)
The Course Instructors were quite friendly.
S(
Sourav (ব্যাচ ৮)
আমি শুধুমাত্র শেখার উদ্দেশ্যেই এই কোর্সটি করেছি, যদিও আমি ইতোমধ্যে আইটি বিভাগে কাজ করছিলাম। তবুও, ওস্তাদ আমার কাছে একটি চমৎকার প্ল্যাটফর্ম মনে হয়েছে। তাদের কারিকুলাম অত্যন্ত সুন্দরভাবে গঠিত, এবং মডিউলভিত্তিক পরীক্ষা গুলো সত্যিই কার্যকর ছিল। আমি ওস্তাদের শিক্ষার মান ও পরিকল্পনায় অত্যন্ত সন্তুষ্ট। 💙
MN
Muhammad Nazmul Alam Kaisar
সাইবার সিকিউরিটির দিকে এগোনোর ইচ্ছে থেকেই আমি এই কোর্সটি করেছি, ওস্তাদ আমার কাছে অন্যতম সেরা একটি প্ল্যাটফর্ম মনে হয়েছে। এখানে অনেক কিছু শিখতে পেরেছি, যা ভবিষ্যতে এই ক্ষেত্রে এগিয়ে যেতে সাহায্য করবে। ওস্তাদের মাধ্যমে শেখার অভিজ্ঞতা সত্যিই দারুণ!
MY
MD. YEASIN AHMED SHUVO
আলহামদুলিল্লাহ, কোর্সটা খুবই ইনফরমেটিভ আর গুছানো ছিলো, অনেক কিছু শেখা গেছে।
AT
Anika Tahsin Rahman
কোর্সটা দারুণ ছিলো! অনেক নতুন কিছু শিখতে পেলাম । বেশ মজা করেই এই কোর্সটা করেছি।
SM
Swagata Mahmud
ওস্তাদ একটি দুর্দান্ত প্ল্যাটফর্ম। কোর্সের সিলেবাস এবং ম্যানেজমেন্ট খুবই উপকারী ছিল। আমি খুব সন্তুষ্ট।
A
Ahsanullah
ওস্তাদ কোর্সের মধ্যে যা শিখিয়েছে, তা সত্যিই আমার কাজের জন্য অনেক সাহায্য করেছে। কোর্সটি খুবই ভালো ছিল।
AH
Arif Hossain
কোর্সটি খুবই ভালো ছিল। আমি কিছু নতুন স্কিল শিখতে চেয়েছিলাম এবং কোর্সটি ঠিক তেমনটাই ছিল, যেমন আমি আশা করেছিলাম।
FR
Faruk Rahman
কোর্সটি অনেক ইনফরমেটিভ ছিল। আমি অনেক নতুন তথ্য শিখেছি যা আমাকে ভবিষ্যতে সাহায্য করবে।
SA
Sakib Al Hasan
Cyber Security বর্তমান সময়ে প্রযুক্তি জগতে অত্যন্ত গুরুত্বপূর্ণ একটি বিষয়। Cyber Security সম্পর্কে বেসিক কিছু আইডিয়া ছিল আমার কিন্তু এই ফিল্ড সম্পর্কে একটি সঠিক গাইডলাইন এবং এই ফিল্ড নিয়ে নিজেকে এক্সপ্লোর করার জন্য আরো কিছু জানার প্রয়োজন থেকেই ওস্তাদের Cyber Security & Ethical Hacking Career Track Program কোর্সটিতে ভর্তি হওয়া। অনেস্টলি, অনেক কিছু জানতে ও শিখতে পেরেছি। যিনি আমাদের প্রশিক্ষক হিসেবে ছিলেন [সাফওয়ান মুনতাসির ভাই] ওনি অনেক সুন্দরভাবে সবকিছু বুঝানোর চেষ্টা করেছেন। মোটকথা, যারা সাইবার সিকিউরিটি নিয়ে ক্যারিয়ার গড়তে চায় বা এই ফিল্ড নিয়ে এক্সপ্লোর করার আগে কিছু শিখতে চান তাদের জন্য একদম পারফেক্ট ও খুবই ফলপ্রসূ একটি কোর্স হবে আশাকরি ইনশাআল্লাহ।
EK
Enayet Kabir
Good learning method.
MO
Mohammad Omar Faruque Tasin (ব্যাচ ১৩)
The course was good and easy for all to understand.
HB
Henry Bapary (ব্যাচ ৯)
The course was very informative.
MM
Md. Mobassirul Islam (ব্যাচ ৮)
Course Instructors প্রত্যেকটা টপিক খুব সুন্দরভাবে বোঝান।
SD
Satirtha Datta (ব্যাচ ১০)
The Course Instructors were friendly and effective, and I consider them good teachers.
SH
Sarowar Hossain Tanmay (ব্যাচ ৯)
The Course Instructors are good explainers.
J(
Junayed (ব্যাচ ৯)
The Course Instructors are very good. I like their teaching method.
AB
Ayan Barua (ব্যাচ ৮)
The Course Instructors teach very well. I hope I can learn even better in the future.
KI
Khayrul Islam (ব্যাচ ৮)
The Course Instructors were very cordial and informative.
SM
Sirajum Monira (ব্যাচ ৮)
The Course Instructors are excellent teachers. In addition, they are very friendly and approachable.
MN
Mohammad Nazmul Haque (ব্যাচ ৮)
সাইবার সিকিউরিটির দিকে ফোকাস করার জন্য আমি এই কোর্সটি করেছি, আমি সদ্য ব্যাচেলর সম্পন্ন করেছি। ওস্তাদ আমার কাছে একটি দারুণ প্ল্যাটফর্ম মনে হয়েছে—একেবারে গোছানো এবং সুন্দরভাবে গঠিত। বিশেষ করে, তাদের নিয়মগুলো খুবই কার্যকর ও সুবিন্যস্ত ছিল। ওস্তাদের কারিকুলাম ও ম্যানেজমেন্ট অনেক ভালো। কোর্সটি সবার জন্য রিকোমেন্ডেড।
DD
Dipto Dutta
আমি শুধু নিজেকে এক্সপ্লোর করার জন্য এই কোর্সে এনরোল করেছিলাম। ওস্তাদ আমার কাছে একটি অসাধারণ প্ল্যাটফর্ম মনে হয়েছে। বিশেষ করে, তাদের নিয়ম এবং ম্যানেজমেন্ট অন্যান্য প্ল্যাটফর্মের তুলনায় অনেক ভালো লেগেছে। একজন পূর্বের শিক্ষার্থী হিসেবে, আমি নির্দ্বিধায় এই কোর্সের এর জন্য সুপারিশ করবো। সবার জন্য এটি দারুণ একটি সুযোগ হবে!
KZ
Kazi Zafar Ahmmed Sabbir
কোর্সটা সত্যিই ভালো ও উপকারি ছিলো। আমি আগেই ওই ফিল্ডে কাজ করছিলাম, তাই আরও স্কিল বাড়ানোর জন্য এই কোর্সটি করেছি। এতে অনেক নতুন কিছু শিখতে ও নিজের স্কিল আপগ্রেড করতে পেরেছি।
MM
Md. Mahfuzur Rahman
ওস্তাদের ক্লাসগুলি অসাধারন ভাবে করানো হয়, খুব ভাল লাগে উনাদের পড়ানোর স্টাইল। প্রতিটা কল্মাষে সব কিছু ইজিলি এক্সপ্লেইন করে দেয়া হয় যেটা পরবর্তীতে বেসিক কনসেপ্ট ক্লিয়ার করতে অনেক সাহায্য করেছে আমার
TH
Tanvir Hassan
এই কোর্সটা আমি নিজের স্কিল বাড়ানোর জন্য করেছিলাম। কোর্সটি সত্যিই ভালো ছিল এবং আমি অনেক কিছু শিখতে পেরেছি।
KH
Kader Hossain
কোর্সটি শেষ করার পর, আমি নিজেকে অনেক বেশি সক্ষম মনে করছি। এটি সত্যিই আমার শেখার অভিজ্ঞতাকে নতুন উচ্চতায় নিয়ে গেছে।
TS
Tasmin Sultana
কোর্সটি অনেক ভালো ছিল। ওস্তাদ খুব সুন্দরভাবে বিষয়গুলো বুঝিয়েছেন এবং শেখানোর পদ্ধতিও অনেক কার্যকর ছিল।
NS
Nadia Sultana
এই কোর্সটি সত্যিই অনেক উপকারী ছিল। আমি শিখেছি এবং জানি, এটি আমার ক্যারিয়ারকে সাহায্য করবে।
NR
Nashit Rahman
আমি একদম বিগিনার লেভেল থেকে সাইবার সিকিউরিটি শিখতে শুরু করেছি। সেই দিক থেকে এই কোর্সটি আমার জন্য অনেক হেল্পফুল মনে হয়েছে। আমাদের ইনস্ট্রাক্টর খুবই সাপোর্টিভ এবং সাহায্য করতে সবসময় প্রস্তুত থাকেন এই বিষয়টি আমাকে সবচেয়ে বেশি অনুপ্রেরণা দিয়েছে। শুধু একটি ছোট প্রস্তাব অ্যাসাইনমেন্ট জমা দেওয়ার সময় আরেকটু বেশি পাওয়া গেলে আরও ভালোভাবে কাজ করে জমা দিতে পারতাম বলে মনে হয়। সব মিলিয়ে কোর্সটি নিয়ে আমি বেশ সন্তুষ্ট এবং শিখতে পেরে সত্যিই খুশি
SS
Sadik Saroar Shovon
কোর্সটি খুবই ভালো এবং সবকিছু বেসিক থেকে জানতে পারছি।
MR
Mobasher Rahman (ব্যাচ ১০)
I like the Course Instructors' attitude towards students.
S(
Sparkle (ব্যাচ ৮)
The course was very informative and well-organized. The Course Instructors explained the topics clearly and made learning engaging and easy to understand. Thank you for the excellent guidance.
SS
Sheikh Sabbir Hossain (ব্যাচ ৮)
The Course Instructors are so supportive and responsible. So friendly!
N(
Nahian (ব্যাচ ১০)
The Course Instructors have the capability to properly explain everything all through. Because of my exams I could not join at the exact time, but when I watched the recordings, they were just as effective as the live sessions.
KC
Koushiq Chowdhury (ব্যাচ ৯)
The Course Instructors' teaching method is so simple and clear that even complex topics are easy to understand. Their patience and dedication are truly inspiring.
MI
Md Ikbal Hossain (ব্যাচ ৯)
The Course Instructors are very friendly.
AS
Ashmit Sadman Bari (ব্যাচ ৮)
The Course Instructors had a strong understanding of the subject and explained concepts in a clear and easy-to-understand way.
JM
Jahin Morshed (ব্যাচ ৮)
The Course Instructors are good mentors.
AT
Ahmed Tajeem (ব্যাচ ৮)
The Course Instructors are very supportive.
AS
Aronna Sarker Uthsa (ব্যাচ ৮)
ভবিষ্যতে এই ক্ষেত্রে কাজ করার ইচ্ছা থেকেই আমি কোর্সটিতে এনরোল করেছিলাম। ওস্তাদ আমার কাছে অন্যতম সেরা একটি প্ল্যাটফর্ম মনে হয়েছে। এখানে আমি অনেক কিছু শিখতে পেরেছি, এবং তাদের ম্যানেজমেন্টও সত্যিই প্রশংসনীয়। একজন পূর্বের শিক্ষার্থী হিসেবে, আমি বলব যে ওস্তাদ একটি দুর্দান্ত প্ল্যাটফর্ম।
FS
Farzana Siddiqui
আমি শুধুমাত্র শেখার উদ্দেশ্যেই এই কোর্সটি করেছি। ওস্তাদ প্ল্যাটফর্মটি আমার কাছে সত্যিই অসাধারণ লেগেছে, বিশেষ করে তাদের কারিকুলাম ছিল একদম পারফেক্ট।
NF
Nasrullah Farhan
ওস্তাদের ক্লাসগুলি অনেক ভালো লাগে ইভেন প্রাক্টিকালি সব বুঝায় দেয়, যেটা আমার পর্বর্তীতে অনেক কাজে লেগেছে। যা শিখেছি মোটামুটি পুরোটাই আত্বস্থ করতে পেরেছি
S
Sourav
আমি সত্যি বলতে বলব, ওস্তাদে কোর্সটি আমার জন্য অনেক সহায়ক ছিল। আমি কিছু নতুন স্কিল শিখতে চেয়েছিলাম, এবং কোর্সটি আমার প্রত্যাশার চেয়েও ভালো ছিল।
RH
Rifat Hossain
কোর্সটা বেশ দারুণ ছিল, এবং ওস্তাদের শেখানোর পদ্ধতি ছিল অনেক ভালো। আমি সত্যিই উপভোগ করেছি এবং অনেক কিছু শিখেছি।
ZA
Zara Ali
কোর্সটি সত্যিই অনেক উপকারী ছিল। আমি এখানে যা শিখেছি তা ভবিষ্যতে আমার ক্যারিয়ারের জন্য অনেক সহায়ক হবে।
FA
Fahim Ahmed
কোর্সটি অসাধারণ ছিল। আমি অনেক কিছু শিখেছি এবং ভবিষ্যতে এটি আমার কাজে আসবে বলে মনে করি।
RH
Rubel Hossain
কোর্সটি খুব ভালো ছিল এবং আমি খুব সন্তুষ্ট। এতে আমার স্কিলস আপগ্রেড হয়েছে এবং অনেক কিছু শিখেছি।
AR
Aminur Rahman
কোর্সটি করতে আমার খুব ভালো লাগছে। আমাদের ইনস্ট্রাক্টর অনেক হেল্পফুল এবং জটিল বিষয়গুলোও খুব সহজভাবে বুঝিয়ে দেন। যেকোনো প্রশ্ন করলেই আন্তরিকভাবে গাইড করেন — যা আমাকে শেখার প্রতি আরও উৎসাহী করে তোলে। অফিসের কাজের পাশাপাশি কোর্সটি চালিয়ে যাওয়া অনেক সময় চ্যালেঞ্জিং হয়ে যায়, বিশেষ করে অ্যাসাইনমেন্ট জমা দেওয়ার সময়কে ম্যানেজ করতে গিয়ে। তবুও সর্বোচ্চ চেষ্টা করছি ঠিকভাবে শিখতে ও নিয়মিত থাকতে। এর বাইরে কোর্সের সবকিছুই আমার কাছে ইতিবাচক মনে হয়। আমি ধারাবাহিকভাবে শেখার চেষ্টা করছি এবং আশা করছি সামনে আরও ভালোভাবে শিখতে পারব।
MN
Md Nahidul Haque
Very practical course, useful for learning.
AJ
Anjum Jahan (ব্যাচ ১০)
I appreciate the Course Instructors' teaching methods.
MM
Mamun Mollah (ব্যাচ ৮)
The Course Instructors are very supportive.
AK
Amit Kumar Bhowmik (ব্যাচ ১০)
The Course Instructors are good and friendly!
MG
Mamun Gazi (ব্যাচ ১০)
The Course Instructors are very supportive.
LK
Lutful Khabir Raufu (ব্যাচ ৯)
The Course Instructors were very friendly and approachable.
HR
Hamidur Rahman (ব্যাচ ৯)
The Course Instructors are very good and well mannered, and they described their lectures throughout the course in a very easy and convenient way.
KR
K.M Rezwan-Ul Islam (ব্যাচ ৮)
The Course Instructors are very helpful.
KA
Khan Abrar (ব্যাচ ৮)
Our Course Instructors are very good people and teachers. Their way of teaching theory is very helpful for our learning.
MS
Mohamed Shariful Islam (ব্যাচ ৮)
The Course Instructors are very supportive and explain perfectly.
HS
HK Siam (ব্যাচ ৮)
সার্টিফিকেট
কোর্স শেষে পেয়ে যান শেয়ারেবল কোর্স কমপ্লিশন এবং এসেসমেন্ট সার্টিফিকেট
 (1).png)
কোর্স কমপ্লিট করে পেয়ে যান শেয়ারেবল কোর্স কমপ্লিশন সার্টিফিকেট
কোর্সে আপনার এসেসমেন্টের রেজাল্টের ওপর পেয়ে যান এসেসমেন্ট সার্টিফিকেট
 (1).png)
প্রায়ই জিজ্ঞেস করা প্রশ্ন

কিভাবে পেমেন্ট করবো?
1. পেমেন্ট মেথড কি কি?
 আপনি সরাসরি ওস্তাদের পেমেন্ট গেইটওয়ের মাধ্যমে Bkash, Nagad, Rocket, Visa, Mastercard, Debit and Credit কার্ড দিয়ে পেমেন্ট করতে পারবেন।
2. আমি কি যেকোনো ডিভাইস দিয়ে পেমেন্ট করতে পারবো?
জ্বী, আপনি ফোন, পিসি কিংবা ল্যাপটপ যেকোনো ডিভাইস দিয়ে পেমেন্ট করতে পারবেন।3. পেমেন্ট প্রসেস কি?
পেমেন্ট করার জন্য প্রথমে ব্যাচে ভর্তি হোন বাটনে ক্লিক করুন। এরপর পেমেন্ট পেইজ থেকে পেমেন্ট মেথড সিলেক্ট করে পেমেন্ট করুন বাটনে ক্লিক করুন এবং পেমেন্ট সম্পন্ন করুন।4. ডিসকাউন্ট কিভাবে পাবো?
আপনি ব্যাচে ভর্তি হওয়ার আগে এভেইলেবল প্রোমো কোড বসিয়ে এক্সপেক্টেড ডিসকাউন্ট পেতে পারেন।5. পেমেন্ট কনফার্মেশন কিভাবে পাবো?
পেমেন্ট প্রসেস শেষ হলে আপনার কাছে একটি মেসেজ আসবে এবং আপনার ড্যাশবোর্ডে আপনার জয়েন করা ব্যাচটি দেখাবে। আপনার স্টাডি প্লান অনুযায়ী কোর্স শুরু করে দিতে পারবেন।6. আমার লেনদেনের হিসাব থাকবে কি?
আপনার ড্যাশবোর্ডে আপনি প্রোফাইল থেকে ট্রাঞ্জেকশন ট্যাবে ক্লিক করে লেনদেন দেখতে পারবেন।
জয়েন করুন আমাদের ফেসবুক গ্রুপে


১,৫০০ জন মেম্বার
Cyber Security Engineers@Bangladesh
ক্যারিয়ার কাউন্সিলরের সাথে কথা বলুন

*সকাল ১০ টা থেকে রাত ১০টা পর্যন্ত
প্রোমো কোড 10-10 ৩৭% ডিসকাউন্ট, আর বাকি ৬ দিন !